
The Liquid Community, a Bitcoin sidechain developed by Blockstream, was drained of roughly 4,000 bitcoin value about $320 million on Sunday. The individual or individuals behind the exploit stated they have been white hat hackers and communicated with Blockstream by messages embedded in Bitcoin transactions utilizing OP_RETURN. The attackers have since returned 3,400 bitcoin to the Liquid federation, whereas preserving 598.5 bitcoin (presently value round $47 million).
The incident doesn’t seem to have concerned compromised keys from the multisig tackle that underpins the community on the bottom Bitcoin blockchain. As a substitute, an obvious bug in Liquid’s node software program allowed attackers to create unbacked Liquid Bitcoin (L-BTC) after which use these cash to set off a legitimate-looking peg-out from the sidechain again to Bitcoin’s base community.
Liquid is a sidechain designed to maneuver bitcoin and different property onto a separate blockchain with sooner transactions and extra options, together with extra personal transactions and asset issuance. It’s operated by the Liquid Federation, a bunch of Bitcoin-focused firms that features exchanges, buying and selling companies, pockets suppliers, and different infrastructure companies. Blockstream develops a lot of the community’s software program and works with the federation on its technical roadmap.
When somebody strikes bitcoin onto Liquid, the bitcoin is locked in a federation-controlled pockets and an equal quantity of Liquid bitcoin, or L-BTC, is created on the sidechain. Liquid is operated by a federation of greater than 80 members, however solely 15 presently function the specialised functionaries on the coronary heart of the community. These functionaries each produce and signal Liquid blocks and safe the bitcoin held in the federation’s 11-of-15 multisig pockets on the bottom Bitcoin community.
The technical particulars of what occurred are considerably sophisticated, however the fundamental gist is {that a} software program bug triggered some Liquid nodes to just accept a transaction that created extra L-BTC than the system truly had backing for.
According to a summary posted to X by pseudonymous Bitcoin industry developer Mononaut, Liquid initially launched a vulnerability associated to the cryptographic proofs used to validate transactions in 2019. Final week, builders tried to repair that problem by way of a software program replace. Nevertheless, that replace additionally apparently launched a brand new bug.
There’s some confusion about what, precisely, was exploited right here.
I’ve seen claims that this was a long-standing bug, exploited after the “repair” was pushed to the open supply repo however earlier than that repair may very well be rolled out in manufacturing.
That doesn’t seem like true.
As a substitute, it… https://t.co/TJeSL7g6kb pic.twitter.com/TazXXpjzWv
— mononaut (@mononautical) September 7, 2026
On Sunday, attackers exploited that flaw. Nodes susceptible to the bug in the up to date software program handled the transaction as legitimate, which allowed the attacker to successfully create roughly 4,000 unbacked L-BTC.
Some Liquid nodes have been apparently working official software program variations that didn’t include the brand new bug. These nodes rejected the exploit transaction and stalled at block peak 4,050,335. Nevertheless, the related nodes concerned with the peg out course of have been, sadly, working the brand new software program.
The newly created L-BTC was then despatched by SideSwap for the peg-out course of, and the federation finally launched roughly 3,996 bitcoin to a Bitcoin tackle managed by the attacker. The Liquid Network’s official X account posted that the SideSwap authorization key and the federation’s different keys weren’t compromised through the assault. The signers did precisely what they have been speculated to do as a result of the software program informed them the peg-out was reputable.
SideSwap’s position in the incident can also be drawing scrutiny as a result of Liquid’s peg-out system is designed to limit withdrawals to approved federation members and whitelisted Bitcoin locations. On this case, nonetheless, roughly 4,000 newly created L-BTC was processed by SideSwap’s peg-out service, ensuing in the federation releasing 3,996 bitcoin to the attacker’s Bitcoin tackle.
Bitcoin security researcher and Liquid member Wiz argued, “If Sideswap broke this strict safety coverage, whereby members are solely allowed to peg-out to offline chilly storage, they’re partly accountable for the theft.”
Different sidechain proposals have tried to handle this sort of drawback with time delays. Programs comparable to Drivechains and Rootstock have mechanisms supposed to present operators extra time to establish and cease suspicious withdrawals earlier than funds go away the system.
Notably, a somewhat similar bug regarding the potential creation of fake cryptocurrency appeared in Zcash earlier this year. A vulnerability in its Orchard shielded transaction system may theoretically have allowed unauthorized creation of ZEC. It was the second such vulnerability with the potential to allow hidden inflation to be found in Zcash’s historical past.
Everybody has to put in it themselves so it is higher than one individual push. However nobody validated shit. Federation would have simply put in code that despatched to blockstream devs personal pockets in the event that they have been informed.
— alp (@alpacasw) September 7, 2026
The flexibility for a code replace from a single celebration to successfully allow this current theft of the bitcoin that backed the Liquid Community has led some to criticize the sidechain’s safety mannequin as decentralization theater. Bitcoin Core contributor Michael Folkson summarized the criticism bluntly on X, posting, “In order I claimed earlier than it’s successfully single sig. Whoever writes and pushes the ‘if legitimate…’ code can transfer the funds. The precise multisig signing is safety theater.”
This idea of decentralization theater has been a rising criticism of the crypto area in normal in current years, as stablecoins, corporate blockchains, and different factors of centralization have led to the trade trying increasingly like the normal monetary system over time and created a crisis of purpose for decentralized general-purpose blockchains.
The Liquid Community additionally had an earlier warning concerning the complexity of its safety structure. In 2020, a timelock bug made roughly 870 bitcoin accessible by an emergency 2-of-3 multisig reasonably than the conventional 11-of-15 federation association. The funds have been by no means stolen, and Blockstream patched the difficulty, however the incident demonstrated that the sidechain’s safety mannequin depends on greater than the 15-member federation.
It stays unclear who’s behind the exploit, however on X, Ledger CTO Charles Guillemet wrote, “They don’t appear to be white hats, and so they don’t appear to be the same old criminals both.”
The attackers repeatedly described themselves as white hats and demanded that the vulnerability be fastened earlier than returning many of the bitcoin, however in keeping with Gart founder Alena Vránová, that doesn’t essentially defend them from authorized penalties. “For those who exploit vuln, steal 4k BTC and demand a repair for ransom, that’s EXTORTION,” Vránová posted on X. “This will imply felony fees and lengthy jail time. Within the U.S. as much as 20 years, and computer-fraud fees can add extra.”
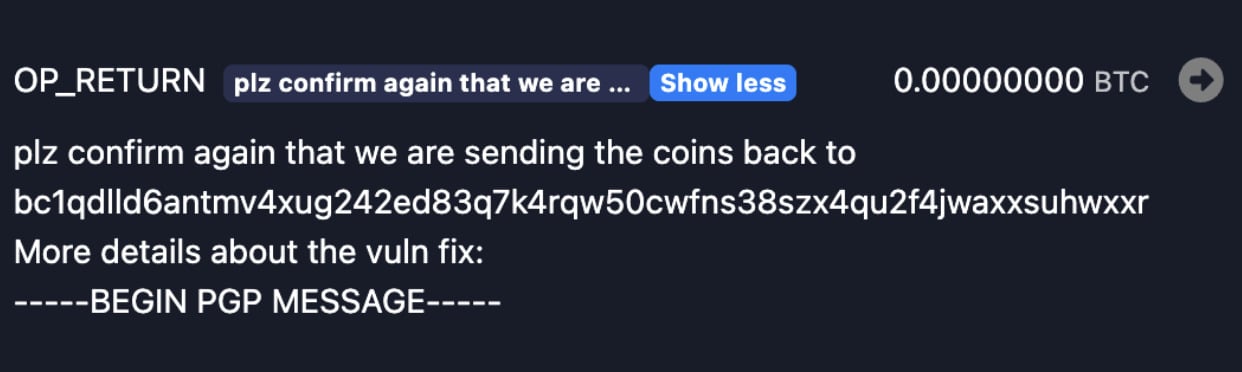
Blockstream finally informed the hackers that the related bridge nodes had been patched, and the hackers have been cautious to confirm the right tackle for returning the funds. Close to the top of their forwards and backwards by way of OP_RETURN transactions, the whole lot of the messages posted to the blockchain have been encrypted by way of PGP. Ultimately, the attacker despatched 3,400 bitcoin again to the Liquid federation tackle and saved 598.5 bitcoin, or roughly 15% of the quantity initially withdrawn, for themself.
It’s presently unclear whether or not AI performed a job in discovering the vulnerability, however crypto has develop into more and more uncovered to AI-assisted hacking this yr. April was the worst month on record in terms of the sheer number of crypto hacks taking place, with practically one incident occurring per day. On X, Mempool’s Orangesurf claimed that Fable 5 may establish the vulnerability behind the Liquid exploit with a five-word immediate.
Liquid was developed by an organization whose founders embrace a few of the earliest Bitcoin builders and Satoshi candidate Adam Again, and the incident comes alongside different current vulnerabilities affecting extremely trusted Bitcoin-related infrastructure, together with a vulnerability exploited for more than $100 million worth of bitcoin in the Coldcard hardware wallet.
Up to now, Bitcoin’s base blockchain and Bitcoin Core software program have remained untouched by this higher wave of exploits hitting crypto. However current occasions have some questioning how lengthy that can proceed. As Japanese Bitcoin researcher and educator Koji Higashi put it in a translated X post, “Bitcoin’s [base blockchain] itself isn’t affected for the time being, but when a significant vulnerability have been to be discovered even there, it’d be critically dangerous, in order that half completely must be defended to the demise.”
The larger drawback for Liquid could also be what occurs now that a big portion of the bitcoin has been returned.
Liquid major belief assumption was based mostly on the truth that it ran for 8 years with some unnamed functionaries (on goal! to not make it a chokepoint).
so, whether or not the funds for liquid get returned or not, there will not be a working Liquid anymore, ie: whether or not the “whitehats” is…
— Nicolas Burtey (@nicolasburtey) September 6, 2026
Cake Pockets COO Seth for Privateness captured the important thing query now hanging over the venture in an X submit, asking, “I feel an unstated vital drawback in all that is . . . who’s going to belief Liquid with their cash?”
Galoy founder and CEO Nicolas Burtey went even additional, writing that no matter whether or not the funds got here again, “they’ve killed Liquid.”