
Researchers on the cryptography analysis agency Alloc Init have proposed a system for bringing Zcash-style non-public transfers to Bitcoin with out requiring a mushy fork.
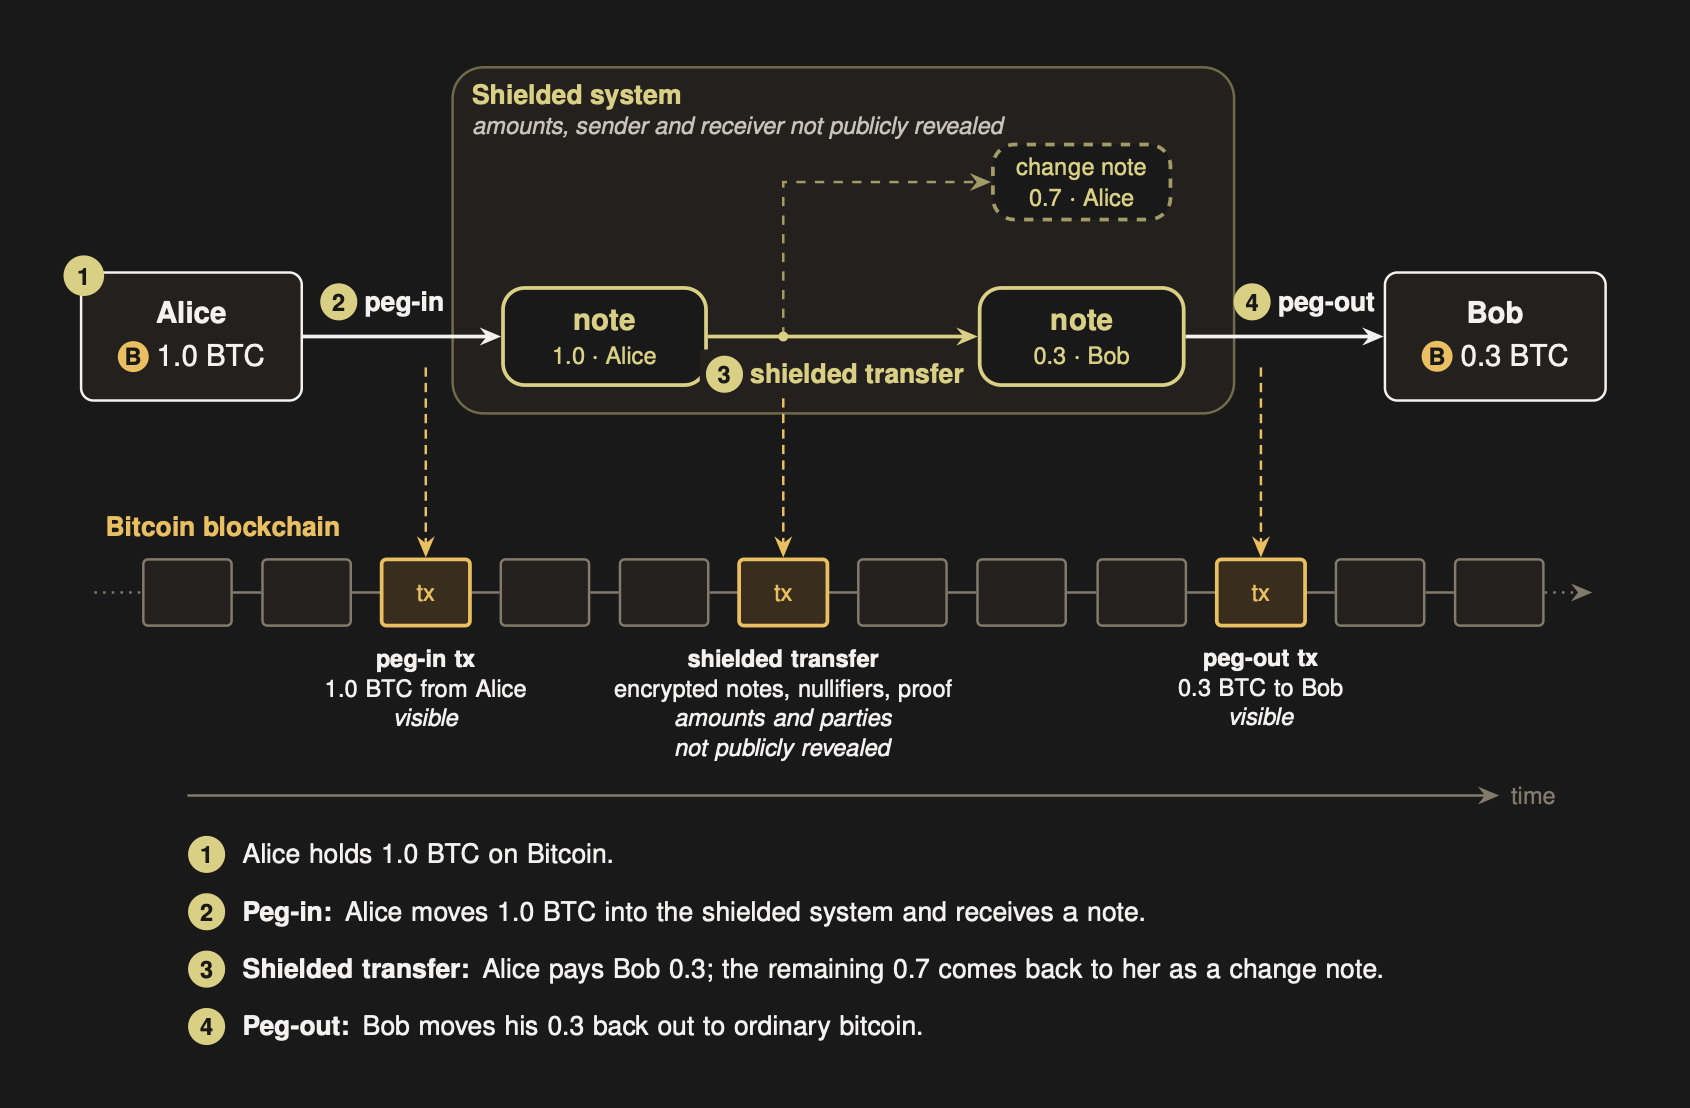
The proposal, called Shielded Bitcoin, would conceal transaction quantities, senders, receivers and hyperlinks to beforehand spent funds utilizing encrypted notes and zero-knowledge proofs. The paper was printed on Thursday by Clara Shikhelman, Mikhail Komarov and Aleksei Moskvin.
The proposal presents a possible path to stronger privateness for Bitcoin customers with out requiring consensus modifications to the bottom protocol.
As a substitute of getting miners implement the privateness protocol, Shielded Bitcoin would use Bitcoin as “a impartial publication and ordering layer,” the researchers wrote. Separate software program known as indexers would then confirm zero-knowledge proofs, test that funds haven’t been double-spent, and reconstruct the state of the shielded system.
Shielded Bitcoin’s design explicitly attracts from Zcash’s structure. The researchers stated it equally makes use of encrypted notes, public nullifiers that mark notes as spent, and zero-knowledge proofs that present transactions are legitimate. Not like Zcash, Shielded Bitcoin wouldn’t function its personal blockchain or consensus mechanism.
Shielded Bitcoin attracts blended reactions
Developer Vadim Zavodil criticized the proposal on X, arguing that a lot of its privateness stack had already been applied by Zcash. He questioned how a lot privateness a newly launched system might initially present, arguing {that a} new shielded pool would begin with out the anonymity set Zcash has collected over years of use.
“Privacy is a perform of the group. Zcash has an actual shielded pool constructed over years,” he wrote. “A model new metaprotocol begins at zero, so your first non-public switch hides in a crowd of 1.”
In a companion submit explaining the proposal, the Shielded Bitcoin researchers acknowledged an identical limitation, saying that enormous deposits don’t routinely create a big anonymity set. They stated observers should have the ability to slim down relationships between transfers if a small variety of actors create most notes or wallets exhibit distinctive conduct.
Associated: Zcash’s November upgrade could freeze funds in legacy Sprout pool
Pierre-Luc Dallaire-Demers, founding father of post-quantum cryptography agency Pauli Group, raised a separate difficulty, describing the development as fascinating however “not quantum resistant in any respect.” Dallaire-Demers later said he was exploring what a totally post-quantum model might seem like, assuming Bitcoin ultimately adopts a post-quantum signature scheme.
Zerocash co-author and StarkWare CEO Eli Ben-Sasson was extra supportive of the proposal’s course. In response to Alloc Init’s announcement, Ben-Sasson said the unique intent behind the Zerocash paper, which preceded Zcash, was to carry privateness to Bitcoin.
Ben-Sasson stated he had not but learn the Shielded Bitcoin paper however want to see the imaginative and prescient of privateness and scalability by way of zero-knowledge proofs materialize on Bitcoin’s base layer.
Journal: Winners and losers of the SEC’s new tokenized stocks rules