
The FBI stated it has disrupted a extremely tailor-made, hard-to-detect cryptocurrency theft scheme by a North Korean hacking group that has managed to steal billions the world over in recent times.
The hackers have aggressively focused folks within the cryptocurrency and Web3 industries, in addition to staff within the improvement and upkeep of open-source software program, the FBI stated in a written assertion. Web3, generally, describes web functions that work together with a blockchain — a digital ledger that shops knowledge.
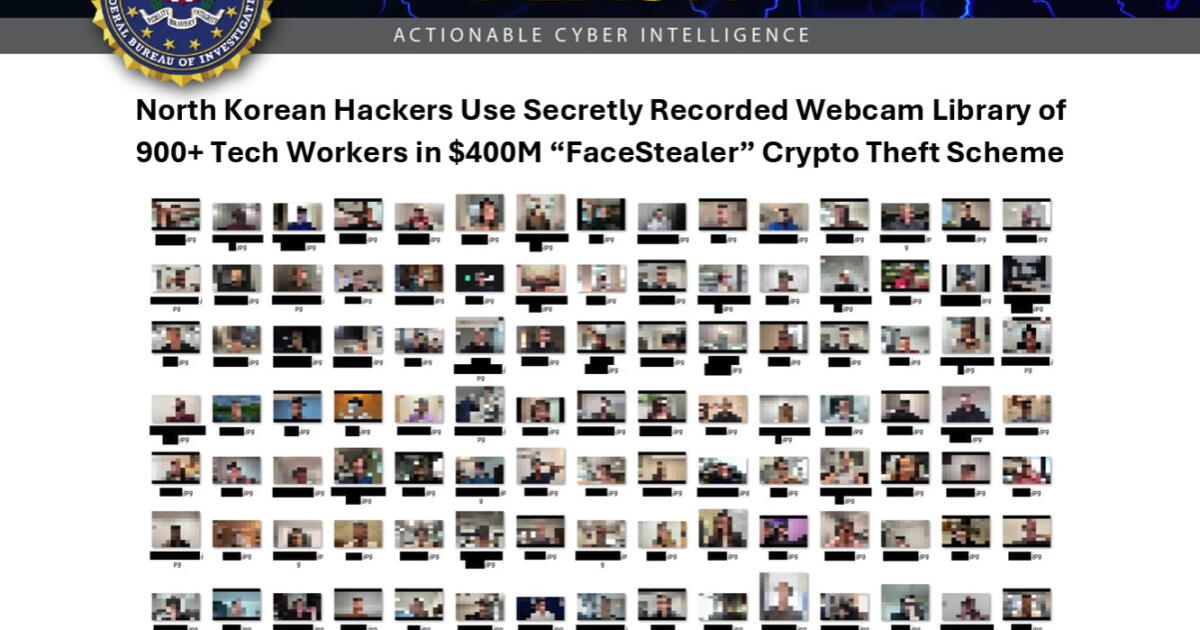
On Thursday, the FBI and Division of Justice announced the disruption of a cloud-based infrastructure used by the North Korean hackers, ensuing within the seizure of greater than 900 webcam movies of victims working within the crypto and Web3 industries worldwide. Earlier than the operation was disrupted, the scheme resulted within the theft of greater than $400 million over an 18-month interval. FBI officers say the funds are used to bankroll its “rogue regime and illicit weapons program by cryptocurrency theft” and the movies are employed to impersonate and goal extra victims.
“North Korea’s authorities bankrolls its rogue regime and illicit weapons program by cryptocurrency theft,” stated Principal Deputy Assistant Atty. Gen. for Nationwide Safety M. Scott Proctor.
“The FBI attributes this exercise to the North Korean hacking group generally referred to within the personal sector as Sapphire Sleet, UNC1069, Stardust Chollima, APT38, and BlueNoroff,” the FBI stated in a written assertion.
“Cryptocurrency sadly has turn into fertile floor for North Korea to defraud victims and fund its malign actions,” Invoice Essayli, the highest federal prosecutor for Los Angeles, stated in a written assertion. “Immediately’s seizure exhibits that America will proceed the combat towards rogue states who financially acquire from cybercrime.”
The federal company stated the hackers used a number of ways to compromise victims, together with a complicated social engineering scheme dubbed “FaceStealer.”
The scheme includes hijacking LinkedIn, Telegram, Slack and Discord accounts of individuals identified to the sufferer, then impersonating these folks to make contact and lure the victims into video calls utilizing Zoom, Microsoft Groups and Google Meets.
Because the sufferer waits for the decision to begin, the hackers secretly file them to impersonate them later. As soon as the decision begins, the impersonator makes an attempt to influence the sufferer to obtain malware, usually below the guise of resolving a technical concern.
“Their goal is compromise of the software program provide chain. By infiltrating accounts of trusted builders and maintainers, the menace actors can probably distribute malicious code by extensively used software program, impacting thousands and thousands of downstream customers,” the FBI stated in its written assertion.
FBI Cyber Department Operations Director Brett Leatherman stated in a press release that the “North Korean regime depends on proceeds from large-scale cryptocurrency theft to fund its illicit weapons program, stealing billions of {dollars} in recent times.”
Individually from the FaceStealer scheme, members of the North Korean navy, referred by the FBI as “TraderTraitor,” stole greater than $6 billion in cryptocurrency from the world’s largest crypto change Binance on Oct. 29, in response to federal authorities. Binance said it has replaced the stolen assets to its prospects, however not recovered the stolen loot.
Federal authorities stated they’ve labored intently with personal corporations to recuperate the stolen funds, freezing greater than $2.7 million and acquiring courtroom approval to grab or prohibit entry to $1.2 billion of that quantity.
FBI officers stated efforts to hint, freeze, seize and forfeit the stolen digital belongings are ongoing. Moreover, the company put out a flash alert on its website to tell the general public of the FaceStealer marketing campaign.