

After suspected North Korean hackers exploited crypto trade Bitget for $387.5 million final week, investigators had been in a position to rapidly flag and hint the recipient addresses.
Bitget CEO Gracy Chen then controversially demanded that decentralized cross-chain swaps platform THORChain “refuse service to those addresses.”
THORChain responded:
“THORChain is decentralized and permissionless like Bitcoin, Ethereum, and BNB Chain. What duty ought to Bitcoin, Ethereum, and BNB Chain bear when dealing with identified stolen funds?”
The transfer was controversial, particularly given the protocol was halted instantly in Might when $10.7 million of its personal funds had been exploited. Complicating issues, THORChain has retired its admin key and claims it doesn’t have a simple option to censor addresses, even when it wished to.
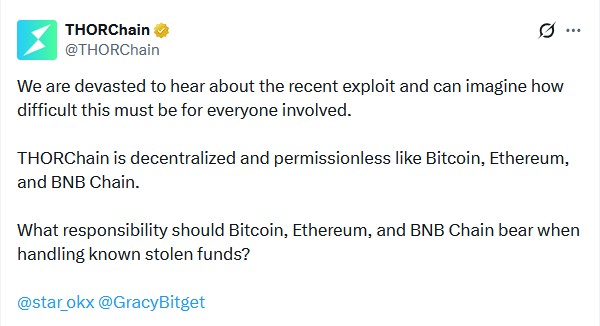
Supply: THORChain
This precise controversy has come up earlier than, as THORChain was used to swap round $1.2 billion of the funds stolen within the $1.46 billion hack of Bybit. It simply so occurred that THORChain’s admin key had been retired simply 11 days earlier.
NEAR Intents took the other strategy to THORChain. Its automated SHIELD program blocked addresses linked to the hack from swapping $50 million on the platform, and even turned down the 5% bounty Bitget was providing for doing so.
Now NEAR Intents is below hearth from decentralization maxis for not being permissionless sufficient.
To debate the authorized points concerned within the case, Journal spoke with Yuriy Brisov from D&A Companions. That is an edited model of the dialog.
Journal: Bitget requested THORChain to dam funds tied to the hack, and it responded saying it’s decentralized and permissionless. Is {that a} authorized protection? Have they got an obligation to dam these addresses?
Brisov: It is determined by the extent of decentralization. So once they do that — once they block some addresses — they present that their nodes aren’t actually decentralized. It’s good for the neighborhood, once they can use this energy to stop some malicious actions. Nevertheless, on the identical time, they open themselves to some other authorized declare. Their solely safety is “we’re decentralized.”
Within the Uniswap case, they mentioned ‘we’re actually decentralized and there may be nothing we will do.’ [Investors sued Uniswap after buying 38 rugpull and scam tokens, but a judge dismissed the case in March —Ed.]
And that is the strongest protection for any DeFi protocol. In the event that they present that they will block, management, or someway intervene — even in a great religion try to stop fraud — they nonetheless open themselves for these sorts of claims. That when you have management, then perhaps your management shouldn’t be restricted to solely apparent fraud instances. You need to suggest [control over] due diligence issues. You need to apply KYC and AML protecting measures.
Associated: Uniswap beats class action alleging it assisted crypto ‘rug pulls’
Journal: NEAR Intents blocked these addresses, and Bitget thanked them for doing so. Does that imply NEAR has proven Intents just isn’t decentralized and can due to this fact have to intervene in numerous different conditions?
In the event you present that you’ve management over belongings, then you definitely probably open your self to all potential claims concerning pump-and-dump schemes, volatility, or some other potential claims of any buyers who someway have been broken and harmed. And so they can now say that you’ve management. Why do you employ it in a single case and never use it in one other case? Why don’t you verify all of your token issuers in your platform? Why don’t they supply KYC varieties like on any centralized trade?
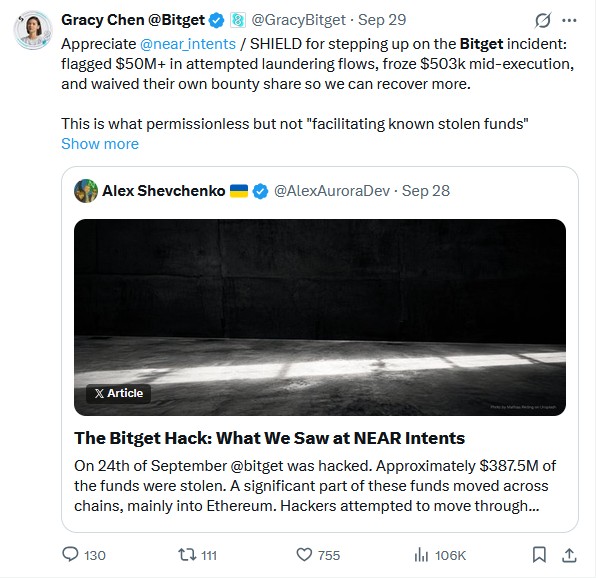
Supply: Gracy Chen
Journal: THORChain argues the protocol halt in Might was initially triggered by an automatic system and that they don’t have the flexibility to dam sure addresses. If true, is {that a} protection?
Brisov: It may be. We don’t know but, as a result of it hasn’t been challenged but. However any quantity of management makes any DeFi mission weaker vis-à-vis any claimant.
Journal: Then again, the protocol might improve the software program if it wished to dam sure addresses. May a mission get in authorized hassle for being reckless or negligent in the event that they don’t impose one thing like that?
It is determined by the way it’s been carried out from the technical facet. Say there may be an oracle that may detect any North Korean IP and block it routinely, and there’s no one who sits and presses a button — “there’s a North Korean hacker, let’s block him.” Then it’s okay.
If there’s a group that oversees the state of affairs and says, “Okay, we will see that is a bootleg exercise, we block these addresses, we press the button manually.” From the authorized viewpoint, although it’s a great act and it advantages the neighborhood, it nonetheless makes the mission not totally decentralized from the authorized perspective, and it strips you of the safety that rules like MiCA [EU’s Markets in Crypto Assets laws] or the overall understanding the SEC and CFTC present that when you’re totally decentralized, you can’t be chargeable for the actions of the individuals in your ecosystem.
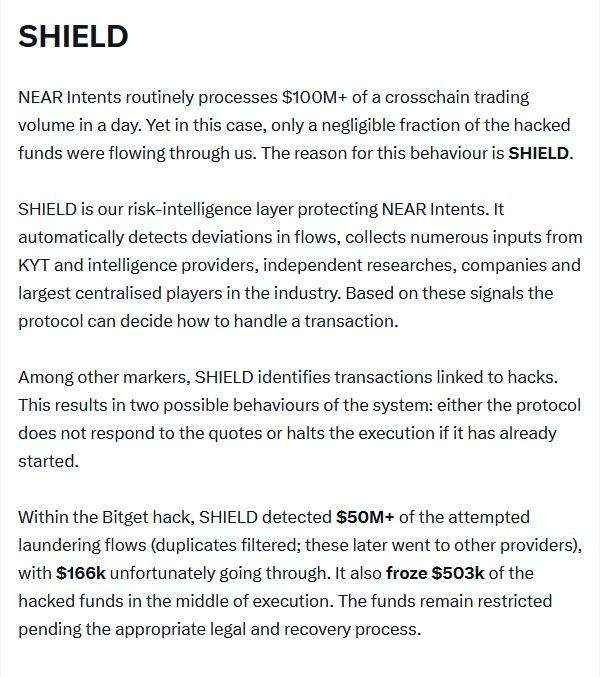
Supply: Alex Shevchenko
Journal: NEAR’s know-how known as SHIELD and it’s an automatic course of that identifies addresses related to identified hacks on public blockchains after which blocks them from accessing Intents routinely. Does that imply it’s extra prone to be seen as decentralized?
Brisov: Undoubtedly. They present that they’re good-faith actors making an attempt to [add] protecting measures into their protocols. There isn’t a compliance group, individuals who sit there and management the operation manually. This can be a good answer, and that’s what we suggest to all of the DeFi firms.
Journal: In February 2025, THORChain retired the admin key which might enable the core group to make these kinds of unilateral modifications. With the dearth of an admin key and the very fact they’ve acquired 100 validators, does that make them sufficiently decentralized?
Brisov: Extra probably than not, however we will’t say that for positive. I might say sure.
Journal: THORChain just isn’t a mixer. You possibly can take stolen Bitget funds and swap them on THORChain, however when it comes out the opposite finish, it can nonetheless be transparently linked to the Bitget hackers. How does that match the definition of cash laundering? Or is it receiving stolen items?
Brisov: I don’t see how they are often chargeable for cash laundering as a result of even Twister Money, that was, to a sure extent, made to launder cash [avoided US sanctions as immutable smart contracts are not sanctionable property in terms of money laundering—Ed].
American regulation treats one thing as both property or not property. And cash laundering is illegally shifting property by way of the authorized channels. You make proceeds of illicit exercise, and it’s property, and then you definitely transfer it by way of some channels and attempt to make it authorized. However good contracts should not property in any respect. You don’t management them. You don’t personal them. That’s how Twister Money received their case in court docket vis-à-vis OFAC sanctions. They simply proved that they don’t have any management over their good contracts.
Journal: The Bybit hack occurred 18 months in the past. Does that imply that no authorized motion goes to be taken in opposition to THORChain, or do these instances simply take a very long time?
Brisov: It would occur sooner or later, undoubtedly. After the Bybit case, they severely opened themselves for potential claims.
Journal: Big Questions: Does Satoshi actually own 1.1 million Bitcoin?
Cointelegraph publishes long-form journalism, evaluation and narrative reporting produced by Cointelegraph’s in-house editorial group with subject-matter experience. All articles are edited and reviewed by Cointelegraph editors in step with our editorial requirements. Some articles include affiliate hyperlinks, from which Cointelegraph could earn a fee. These relationships don’t affect which merchandise we evaluation or our editorial conclusions. Content material revealed in right here doesn’t represent monetary, authorized or funding recommendation. Readers ought to conduct their very own analysis and seek the advice of certified professionals the place acceptable. Cointelegraph maintains full editorial independence.

Cointelegraph by Andrew Fenton Does THORChain Face A Criminal Reckoning Over Stolen Bitget Funds? cointelegraph.com 2026-09-30 13:30:00
Source link