
The staff behind Core Lightning, an open-source node software program for the Bitcoin Lightning Community, has urged operators working older variations to improve instantly after receiving experiences of attackers concentrating on unpatched nodes.
“Pressing safety replace: When you’re working model 26.06.7 or earlier, please improve to the newest launch as quickly as doable,” the staff said on Friday.
Core Lightning didn’t specify which vulnerabilities attackers have been concentrating on or the potential affect. Cointelegraph reached out to Core Lightning for remark.
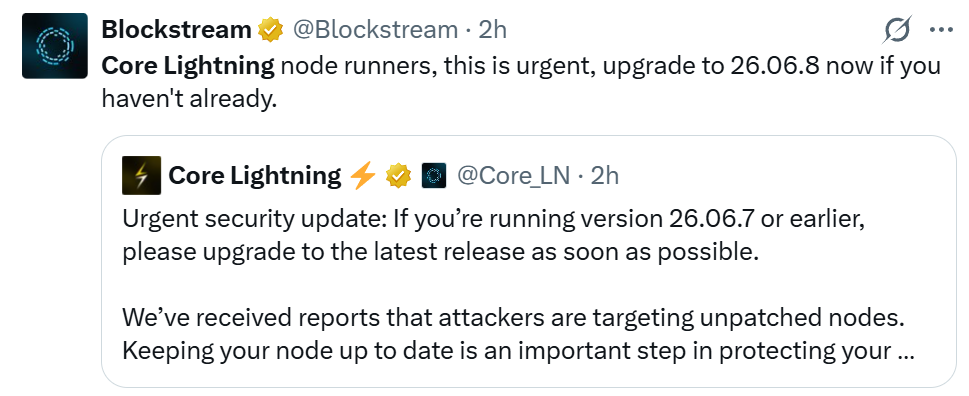
Supply: Blockstream
On Sept. 16, Core Lightning stated it was investigating experiences of a possible situation affecting experimental options in Core Lightning that might affect consumer funds. It then launched model 26.06.8 round six days later.
The Sept. 22 replace delivered bug fixes alongside patches for “vulnerabilities responsibly reported by a quantity of sources.” The discharge notes credit score the Bitcoin Purple Workforce and 12 different named people and teams, together with nameless reporters.
Some of the fixes addressed flaws that might crash senders’ nodes, requests that might exhaust reminiscence in its REST interface and a channel-closing bug that might trigger customers to lose funds to a penalty, based on the changelog.
Nevertheless, the discharge intentionally withheld some checks to make it more durable for attackers to reverse-engineer and exploit vulnerabilities whereas operators upgraded.
In August, Core Lightning stated it was working on a coordinated repair after assessing a excessive quantity of AI-generated Widespread Vulnerabilities and Exposures (CVE) experiences over current weeks.
Two days later, it launched 26.06.7 to handle the confirmed vulnerabilities.
Associated: Core Lightning confirms multiple vulnerabilities, prepares security update