A coding task from a potential employer appeared like an peculiar a part of a job interview. As a substitute, it was one step in a months-long cyberattack that ended with $6.3 billion stolen from Binance, elevating questions on how exchanges shield themselves in opposition to threats that focus on their staff.
The assault was a part of a coordinated marketing campaign that exploited each human vulnerabilities and inner safety methods, based on a postmortem launched by Binance on Tuesday. The trade’s findings detailed how hackers step by step gained entry to its pockets infrastructure earlier than the Oct. 29 theft.
How hackers infiltrated Binance
In line with Binance’s safety report, the assault marketing campaign started in June, when an engineer downloaded a tampered software program package deal whereas organising an AI coding device. Though Binance detected the malware and changed the affected machine, the attackers had already gathered details about the trade’s pockets crew.
In September, attackers posing as recruiters focused one other software program engineer and tricked the worker into downloading a malicious file disguised as a coding task. The malware compromised the engineer’s work pc and evaded the trade’s safety protections.
On Oct. 20, the attackers used the compromised pc and an inner AI device to realize entry to 2 extra engineers’s methods, acquiring deployment credentials that allowed them to put in malicious software program inside Binance’s pockets infrastructure on Oct. 29.
The attackers then gained entry to the trade’s inner wallet-signing service, which authorizes cryptocurrency transactions. This allowed them to maneuver funds outdoors the traditional withdrawal course of.
“This wasn’t one mistake or one breach — it was a months-long marketing campaign,” Binance co-CEO Richard Teng mentioned in a Tuesday post on X.
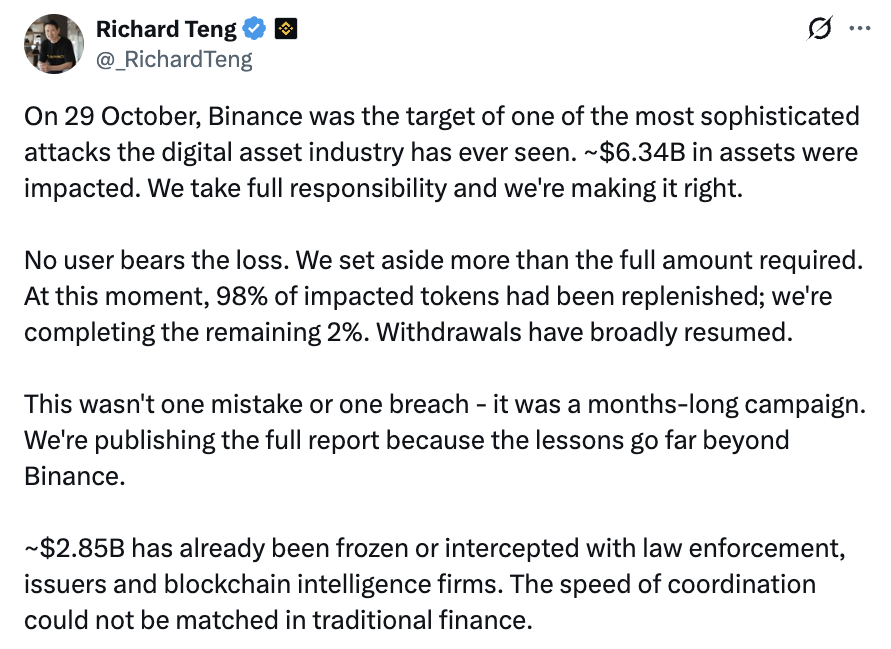
Supply: Richard Teng
Binance mentioned the attackers additionally exploited Ethereum’s EIP-7702 mechanism, which permits wallets to delegate transaction permissions to good contracts, enabling unauthorized transfers to proceed even after the trade suspended withdrawals. Its multiparty computation (MPC) pockets system, which distributes management over transaction signing, difficult efforts to revoke these permissions.
The breach affected roughly $6.3 billion in digital assets, with Binance reporting that $2.85 billion had been frozen or intercepted, based on its newest accounting. The trade mentioned it will soak up the losses relatively than move them on to prospects and had replenished 98% of the affected token property as of Oct. 31.
The assault, the most important cryptocurrency hack in historical past, has been attributed to North Korean hackers by the Federal Bureau of Investigation (FBI). On Tuesday, Kim Yo Jong, the sister of North Korean chief Kim Jong Un, denied the country’s involvement, saying the FBI’s attribution was politically motivated and supposed to break North Korea’s worldwide standing.
Binance reviews 57 cyber threats blocked this yr
Binance co-founder Yi He said Tuesday that the trade’s safety crew had detected and prevented 57 suspected North Korea-linked cyber threats in 2026, together with fraudulent job interviews, malicious software program packages and social engineering makes an attempt aimed toward stealing credentials or putting in malware.
“We intercepted lots of them, however the price of failing to cease even one was extreme—and this could by no means have occurred,” she mentioned.
Journal: Binance hackers raced to move billions before it could be frozen
Cointelegraph by Nate Kostar Binance Details Security Failures Behind Record $6.3B Crypto Hack cointelegraph.com 2026-11-03 16:44:06
Source link