Vitalik Buterin is shifting a few of his Ethereum exercise out of web site interfaces. In his October 31 essay, the Ethereum co-founder mentioned he had used an AI-written command-line instrument for latest IPFS content-hash updates on ENS, Ethereum’s naming system, and kohaku-cli, a command-line pockets, for many payments by way of privateness protocols. The ENS updater and cost pockets have been separate instruments.
His objection goes past display muddle. An internet site can ship software code once more every time somebody returns, leaving the person depending on what the server provides every time. Holding a neighborhood software can cut back that repeated supply publicity. It additionally strikes a consequential determination onto the person: which software program revision to put in, retain and finally substitute.
The pockets he linked makes the trade-off concrete. Its documentation warns that the CLI is unaudited, beneath energetic improvement and written with AI help. It tells customers to keep away from mainnet except they perceive what they’re doing and the potential of catastrophic fund loss.
Management over a downloaded interface issues as a result of the accepted code sits between a cost instruction and the signature authorizing it. Selecting when that code modifications can cut back one recurring publicity, whereas its dependencies and signing entry decide what the put in software program can do.
Holding a replica modifications the supply determination
The sensible acquire is the power to maintain a selected software revision slightly than acquiring the web site interface once more on every go to. Accepting a alternative revision creates one other supply determination. For this source-build route, that call additionally includes the dependency set and the instruments that flip supply into executable software program. A well-known undertaking title alone doesn’t describe all of the code being accepted.
Kohaku-cli handles public Ethereum accounts and private balances on Twister Money, Railgun and Privateness Swimming pools V1. It’s a specific pockets software, distinct from the broader Kohaku toolkit of reusable protocol libraries and pockets infrastructure. Its warning needs to be learn at that software stage, slightly than as an audit verdict on each element or protocol it uses.
The documented set up route additionally reveals what “native” entails. The undertaking’s directions name for putting in dependencies with npm set up, constructing the applying with npm run construct, and operating a neighborhood launcher. At commit 0ef5c44, the documentation, manifest, lockfile and implementation describe the identical software revision. Its manifest identifies model 0.1.0 and requires Node.js 22 or later. Buterin’s account doesn’t determine his put in revision.
The manifest fixes direct dependency variations, together with viem and a number of other Kohaku packages. It additionally pins a separate kohaku-artifacts Git dependency to a commit. The corresponding lockfile information resolved registry packages and integrity hashes. The appliance due to this fact has a software program provide chain even when its interface runs on the person’s machine.
Preparation can already contain a signature
Kohaku-cli’s public-transfer and Railgun unshield paths present why a pause earlier than submission can imply various things. An bizarre public-transfer dry run returns with out sending the transaction; a ready Railgun unshield can already include a signature.
For an bizarre, non-batched public switch, the transfer implementation simulates the transaction and returns dry-run output with out submission. The printed path requires the sender’s private key, constructs a neighborhood pockets shopper and sends the transaction. The wallet-client code derives its signing account from that private key.
Private operations expose a further wrinkle. The unshield command can output a ready Railgun UserOperation that’s already signed, even when broadcasting is withheld. A UserOperation is an account-operation payload that suitable tooling can submit. The separate broadcast implementation expects a signed operation after which sends it by way of a Pimlico bundler.
For that path, withholding submission can nonetheless depart a signed operation prepared for suitable tooling to submit later. Calling the outcome “ready” due to this fact doesn’t make it universally unsigned. Software program that will assemble an authorization, software program that will signal it and software program that will submit it have to be assessed as distinct sources of authority, even when one CLI coordinates them.
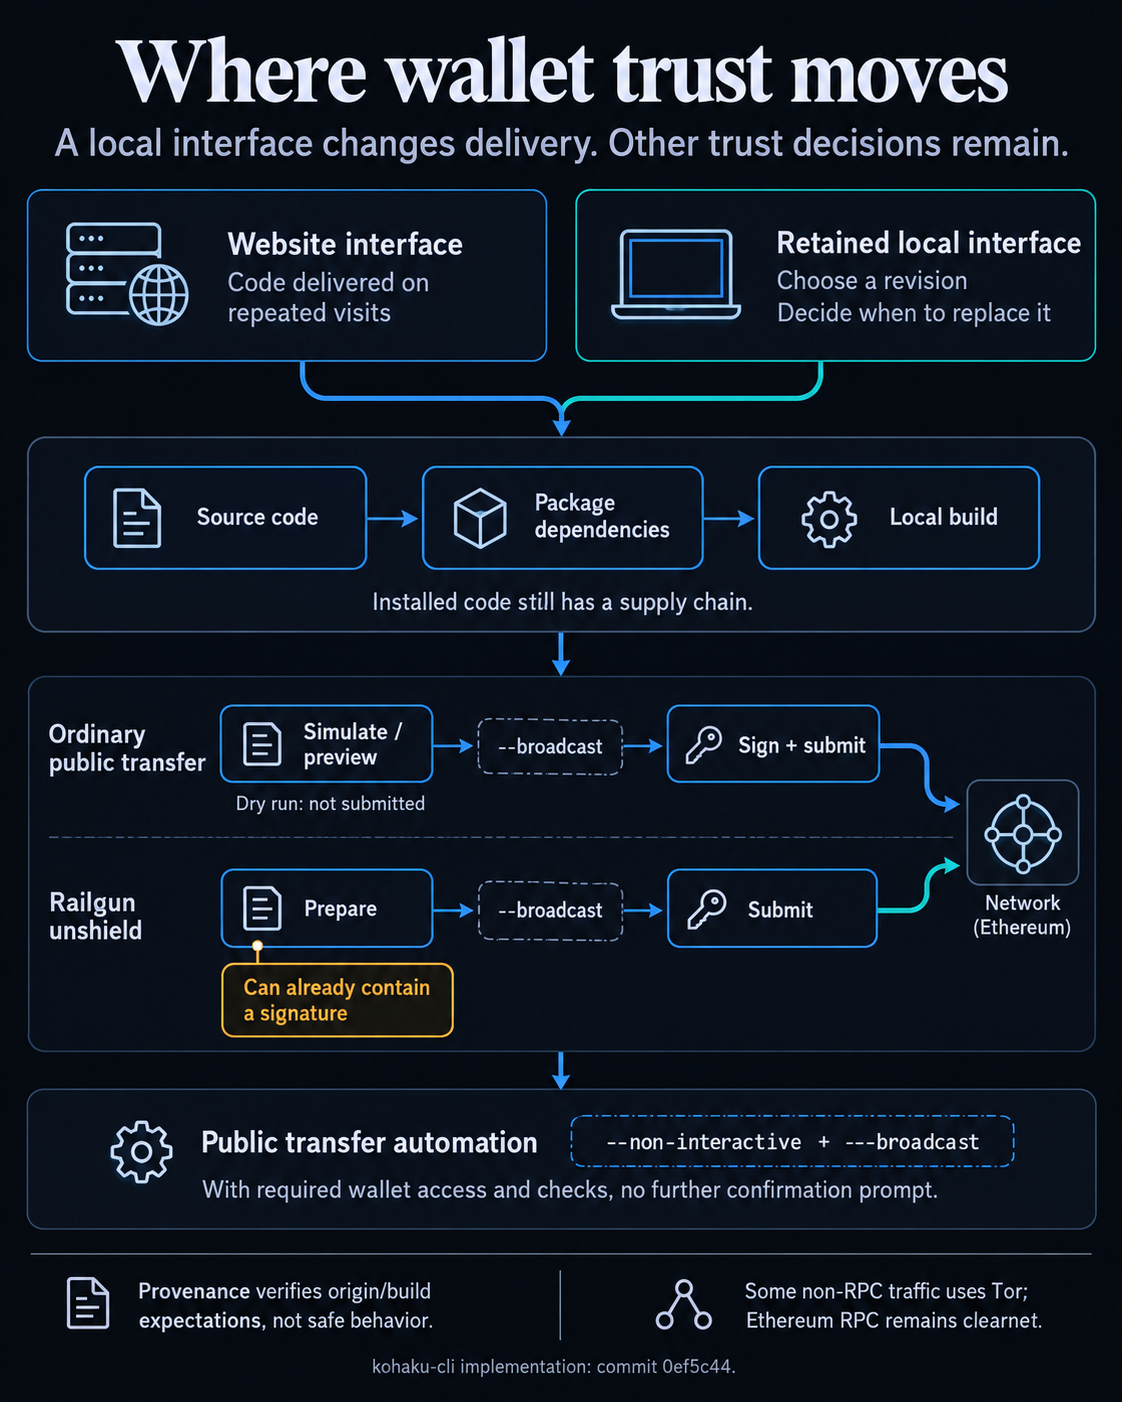
Human affirmation is one other separate alternative. Within the inspected public-transfer path, a suitably configured caller with pockets entry can use --non-interactive along with --broadcast to submit with out a additional affirmation immediate. Pockets unlocking, required parameters, chain matching and simulation checks nonetheless apply. The potential is related to scripts and brokers; it doesn’t reveal whether or not Buterin uses unattended payments.
The README describes an encrypted seed on disk and owner-restricted password recordsdata for POSIX automation. These measures govern saved secrets and techniques and the way a course of obtains entry to them. They don’t, by themselves, set up an impartial spending restrict or recipient coverage as soon as the method can use the signer.
CryptoSlate has beforehand coated the wallet-permission problem for local AI. Supply management provides one other dimension: a person can retain a selected interface revision, whereas that code operates inside no matter signing and submission authority it receives.
Provenance checks origin, with a separate query about conduct
Software program provenance affords a strategy to look at the supply facet extra rigorously. It information the place an artifact got here from and the way it was constructed. The SLSA verification standard describes checking a provenance signature, matching the artifact’s digest, recognizing a trusted builder and evaluating the said supply and construct parameters with anticipated values.
These checks may also help distinguish an anticipated construct from a substituted artifact or an unintended construct supply. They nonetheless depend upon which builders and supply expectations the verifier trusts.
Dependency checking stays its personal activity. SLSA describes recursive verification of resolved dependencies as an non-obligatory extra step. Authenticating the top-level artifact doesn’t robotically authenticate each enter to it.
Appropriate origin and construct historical past can accompany software logic that the person would nonetheless reject.
Community privateness is equally separate from software supply. The CLI documentation describes Tor by default for sure non-RPC visitors whereas Ethereum RPC stays on the bizarre community connection. Working the interface regionally due to this fact doesn’t make each exterior interplay private. Earlier Kohaku and verified-RPC coverage involved one other a part of this broader belief downside.
Buterin’s experiment factors to a concrete type of person management: selecting the applying code that stays on the machine and deciding when to just accept alternative code. Its worth will depend on carrying that management by way of dependency choice and the signer.