

Key takeaways
- On October 29, 2026, an attacker moved roughly USD 6.36 billion out of Binance wallets on ten blockchains, most of it in about 20 minutes beginning at 20:05 UTC. That makes this the largest crypto theft on report, about 4 instances the USD 1.5 billion Bybit hack of February 2025. Binance has confirmed a safety incident and suspended withdrawals on a number of networks.
- TRM attributes the assault to TraderTraitor, North Korea’s elite hacking unit, based mostly on sturdy on and off-chain intelligence. We make this judgment with excessive confidence. TRM is monitoring the funds and alerting companions by the Beacon Community.
- On Ethereum, the attacker used an EIP-7702 delegation to show a Binance sizzling pockets right into a sweeper it managed, with 50 pre-signed authorizations ready in advance. In the identical window, Binance wallets on the different 9 chains despatched funds to the attacker by atypical signed transfers. In TRM’s evaluation, this factors to a compromise of Binance’s sizzling pockets signing infrastructure.
- Tether, Circle, Ripple and World Liberty Monetary froze about USD 2.67 billion in stablecoins, and Arbitrum’s Safety Council froze 8,426 ETH and 74.6 million ARB on its community, for a complete of roughly USD 2.7 billion. The attacker raced the freezes by promoting USDT to market makers and borrowing ETH towards USDT on Aave. It now holds greater than 420,000 ETH and 18,270 BTC, about USD 2.4 billion in property past any issuer’s attain.
What occurred
On the night of October 29, billions of {dollars} in crypto started leaving wallets belonging to Binance, the world’s largest cryptocurrency trade. Inside minutes, Binance wallets on the XRP Ledger, Ethereum, Bitcoin, Tron, Solana and 4 different networks had despatched their balances to addresses managed by a single attacker. A second wave round 23:05 UTC reached Binance wallets on Avalanche and Polygon.
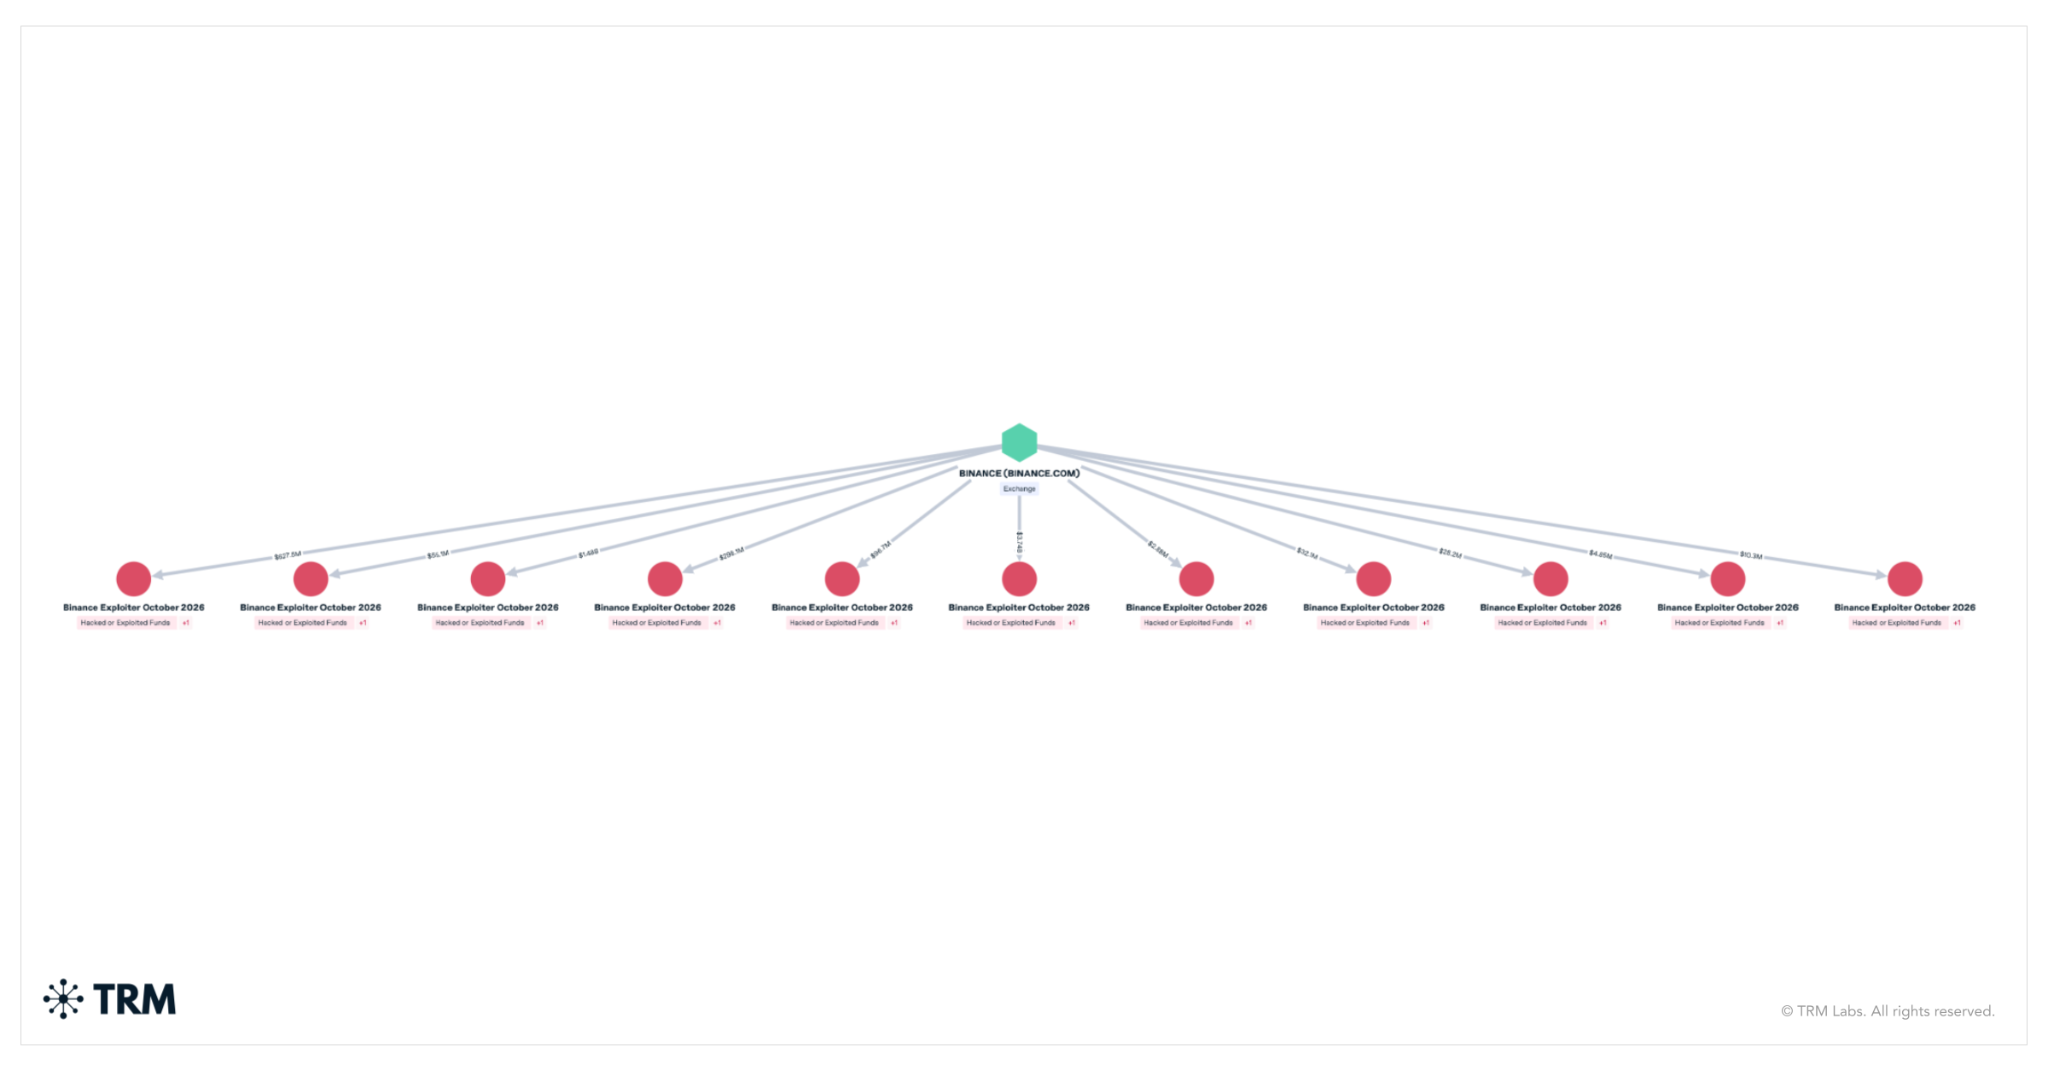
Binance mentioned it was investigating a possible safety problem, then mentioned it had quickly suspended withdrawals on a number of networks as a precaution. Binance has mentioned person funds are protected. The story remains to be creating, and the figures right here replicate what TRM noticed onchain as of October 30 at 00:30 UTC.
Who’s behind it
TRM attributes this assault to TraderTraitor, North Korea’s premier hacking unit. We base this evaluation on sturdy on and off-chain intelligence sources. The FBI named the identical group as liable for the USD 1.5 billion Bybit hack in February 2025. A number of options of this assault match earlier North Korea-linked heists, together with the Bybit hack and the KelpDAO hack in April 2026: small Twister Money withdrawals funding an operator pockets, staging that started effectively earlier than the theft, and signatures obtained in advance then executed in one burst. The laundering noticed up to now, constructed on massive swaps by market makers and lending protocols, differs from the bridge-heavy sample that adopted Bybit. TRM will share additional findings as the investigation develops.
How a lot was taken
TRM traced each switch from Binance-attributed wallets to attacker-controlled addresses throughout ten blockchains. Valuing every switch at the worth of the asset at the second it was taken, the whole is roughly USD 6.36 billion. At present costs, the identical property are price about USD 6.23 billion.
Ethereum accounts for about USD 3.79 billion. That features 200,630 ETH and 185 different tokens, amongst them 1.875 billion USDT, 823 million USDC and 88.5 million RLUSD. Bitcoin outflows whole 18,270 BTC, about USD 1.47 billion. Tron outflows whole 612.7 million USDT and 46.4 million TRX, about USD 628 million. The XRP Ledger misplaced 233.46 million XRP, about USD 296 million. Solana outflows whole 970,500 SOL, about USD 96 million. Arbitrum, Optimism and Base mix to about USD 39 million, together with 74.6 million ARB taken on Arbitrum. Avalanche outflows whole about USD 28 million, and Polygon outflows whole about USD 10 million.
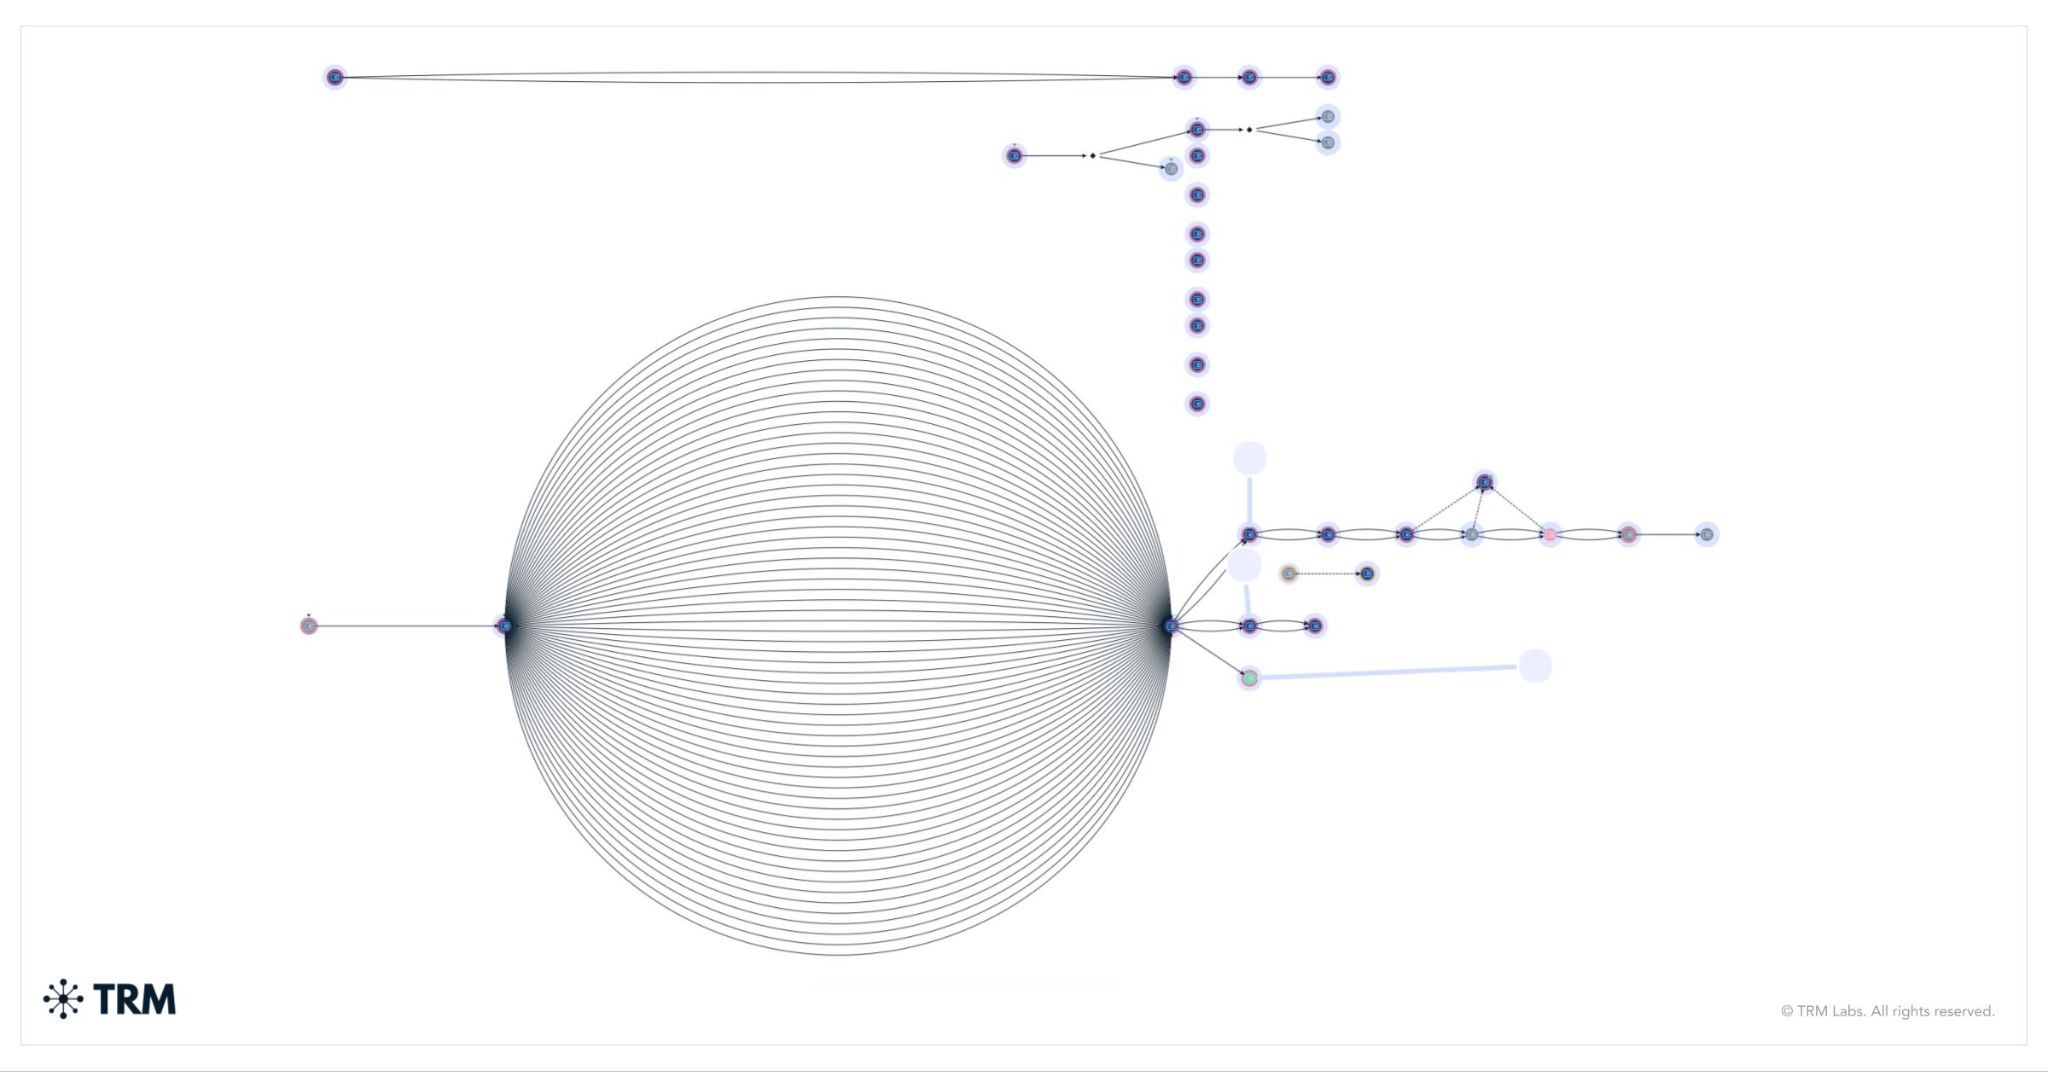
How the assault unfolded
Preparation started not less than 36 hours earlier than the theft. The attacker’s operator pockets obtained three small withdrawals from Twister Money, a service that obscures the place crypto comes from, beginning the morning of October 28. Early on October 29, the operator deployed a primary piece of code for the assault and examined it on two wallets. Later that day, it rehearsed the remaining model on a 3rd pockets, then routed the check funds again to itself. 4 hours after that rehearsal, the identical code was put in on a Binance sizzling pockets.
The primary theft of the evening got here on the XRP Ledger. Between 20:05 and 20:09 UTC, 5 Binance wallets despatched 233.46 million XRP to a single attacker tackle, leaving every pockets with solely its minimal steadiness. That XRP has remained in place since. Binance wallets on Solana and Optimism adopted shortly after 20:10 UTC. At 20:20 UTC, a Binance Bitcoin sizzling pockets despatched 18,270 BTC to an attacker tackle, which started splitting the funds into spherical 1,000 BTC and 100 BTC items inside the identical block. That method, referred to as a peel chain, makes funds tougher to observe. Inside two minutes, a Binance sizzling pockets on Tron despatched 612.7 million USDT and 46.4 million TRX to the attacker.
How the attacker took over a Binance sizzling pockets
A sizzling pockets is a pockets linked to the web that an trade makes use of to course of buyer withdrawals. The Ethereum sizzling pockets in this case is one among the best-known Binance wallets.
EIP-7702, launched in Ethereum’s Pectra improve in Might 2025, permits an atypical pockets handy management of its habits to a wise contract by signing an authorization. From then on, each name to the pockets runs that contract’s code, and the association stays in place till the pockets indicators a brand new one.
At 20:20 UTC, the operator submitted a single transaction containing 50 authorizations. Every was signed by the Binance sizzling pockets, and every pointed it to a sweeper contract that accepts directions solely from the operator. Each pockets retains a operating depend of its transactions, referred to as a nonce, and an authorization works solely at the depend the pockets has reached at the second it executes. The Binance sizzling pockets processes a gradual stream of withdrawals, so its depend retains transferring ahead. By getting ready signatures for 50 consecutive counts, the attacker assured that one would nonetheless be legitimate when the transaction executed. One matched, which was all the attacker wanted. The signatures have been produced in advance as a batch.
Three minutes and 24 seconds after the delegation, the operator instructed the Binance sizzling pockets to ship its whole steadiness to an attacker-controlled tackle. That single transaction moved 167,464 ETH and 63 tokens, together with 1.615 billion USDT.
The delegation remained in place. As new funds reached the Binance sizzling pockets, the operator swept them once more at 20:41, 20:59, 21:04, 21:44, 22:39 and 23:56 UTC. The pockets additionally served as the executor of a separate Binance sensible account, which gave the attacker the potential to tug 823 million USDC from it. Circle froze that USDC shortly afterward.
Proof factors to Binance’s signing infrastructure
Early indicators on the Ethereum exercise urged the attacker had phished the authorizations. That rationalization covers Ethereum and leaves the different chains unexplained. In the identical window, 5 Binance wallets on the XRP Ledger, Binance wallets on Arbitrum, Avalanche, Optimism and Base, a Binance Bitcoin sizzling pockets, a Binance sizzling pockets on Tron and a Binance pockets on Solana despatched funds to the attacker by normal signed transfers. One other Binance sizzling pockets on Ethereum despatched 28,006 ETH, 55.7 million USDT and 25.9 million RLUSD the identical manner, with none delegation. About two and a half hours later, at 23:05 UTC, Binance wallets on Avalanche and Polygon adopted.
These wallets use totally different chains, key sorts and signing schemes. All of them produced legitimate signatures for the attacker inside about half an hour. In TRM’s evaluation, the probably rationalization is that the attacker gained the potential to make Binance’s sizzling pockets signing system signal transactions of its selecting throughout chains. The batch of fifty pre-signed authorizations suggests the entry could have been restricted in time, or that signatures needed to be requested by a system. Binance has but to publish a root trigger.
Stablecoin freezes and conversion
Stablecoin issuers moved rapidly, and the freezes saved spreading by the evening. Binance mentioned at 23:35 UTC that the verified whole frozen had reached USD 2.54 billion. Together with later freezes, TRM counts about USD 2.7 billion frozen onchain as of 00:30 UTC:
- Tether, about 1.77 billion USDT. Tether froze 971.1 million USDT in the foremost receiving pockets at 21:01 UTC, 37 minutes after the foremost sweep. Later sweeps landed in the frozen pockets, which now holds 1.175 billion USDT. Tether additionally froze 205 million USDT in two different attacker wallets on Ethereum, 378.7 million USDT in two attacker wallets on Tron and eight.4 million USDt on Avalanche. One other 6.2 million USDT0 on Polygon is frozen as effectively.
- Circle, about 825 million USDC. Circle froze the 823 million USDC in the foremost receiving pockets at 21:04 UTC, in coordination with regulation enforcement. It later froze 1.56 million USDC that the attacker had swapped from AVAX and bridged from Avalanche to Ethereum.
- Ripple, 40.5 million RLUSD. Ripple froze the pockets holding the stolen RLUSD at 22:01 UTC, with 40.5 million of the 88.5 million RLUSD nonetheless inside. It additionally froze RLUSD in the compromised Binance sizzling pockets, so new deposits couldn’t be swept. Binance co-CEO Yi He mentioned Ripple helped cease about USD 200 million from transferring; TRM has confirmed the 40.5 million RLUSD freeze onchain.
- World Liberty Monetary, 27.8 million USD1. World Liberty Monetary froze the 27.8 million USD1 in the foremost receiving pockets at 22:10 UTC, and froze USD1 in the compromised Binance sizzling pockets at 22:26 UTC.
- Arbitrum Safety Council, 8,426 ETH and 74.6 million ARB. Arbitrum’s Safety Council is a bunch that may take emergency motion on the Arbitrum community. At 00:08 UTC, it used these powers to drive two transfers out of the attacker’s pockets on Arbitrum, transferring 8,426 ETH and 74.6 million ARB, about USD 30 million, out of the attacker’s attain.
Throughout the first hours, the attacker transformed freezable stablecoins into property past any issuer’s attain, at steep price. About 325 million USDT was offered to skilled fillers and market makers by UniswapX and different intent-based contracts in trade for about 122,300 ETH. That means a worth close to USD 2,650 per ETH when ETH traded round USD 2,300 to 2,350, a reduction of greater than 10%. The remaining 175 million USDT from that batch was frozen.
A second attacker pockets equipped 60 million USDT to the lending protocol Aave and borrowed about 19,760 ETH towards it, after which Aave froze the affected markets. On Tron, 300 million USDT moved to a pockets that started supplying it to the JustLend lending protocol. An extra 200 million USDT moved by a sequence of hop wallets that swapped it on Uniswap, and 30 million USDT from that chain was frozen. The 88.5 million RLUSD handed by two hops to a pockets that offered 48 million of it by decentralized exchanges between 21:42 and 22:01 UTC, till Ripple froze the remaining 40.5 million.
With the ETH consolidated in a couple of wallets and the 18,270 BTC transferring by the peel chain, the attacker controls about USD 2.4 billion in property past any issuer’s attain. Primarily based on earlier massive thefts, TRM expects the subsequent stage to contain cross-chain bridges, swap providers and over-the-counter brokers. TRM is monitoring the peel chain outputs and the consolidation wallets for these actions.
What exchanges and compliance groups ought to do now
Exchanges and compliance groups ought to display deposits and counterparties towards the attacker addresses TRM has labeled. Funds from the Bitcoin peel chain and the ETH consolidation wallets are prone to attain exchanges, swap providers and OTC desks in the coming days.
Treasury groups ought to monitor Ethereum-compatible wallets for EIP-7702 delegations, which seem as code at an tackle that ought to have none. Any such delegation on a treasury pockets ought to set off a direct alert. Groups ought to maintain a examined, pre-approved technique for signing a revocation.
Signing insurance policies ought to reject EIP-7702 authorizations except they’re anticipated. A request for a lot of authorizations throughout a variety of transaction counts ought to be handled as an indicator of compromise. Signing infrastructure and approval paths ought to be separated by chain and pockets tier. On this incident, a single actor obtained legitimate signatures for wallets on ten chains inside hours.
Market makers and solvers ought to display counterparties earlier than filling massive orders. About 325 million USDT was offered to market makers and solvers by a pockets that had obtained it from the hack minutes earlier. Actual-time tackle screening would have flagged it.
Steadily requested questions
- What occurred to Binance?
On October 29, 2026, an attacker moved roughly USD 6.36 billion out of Binance wallets on ten blockchains, together with Ethereum, Bitcoin, Tron, the XRP Ledger, Solana, Arbitrum, Avalanche, Optimism, Base and Polygon. Binance confirmed a safety incident and suspended withdrawals on a number of networks.
- Who’s behind the Binance hack?
TRM attributes the Binance hack to TraderTraitor, a North Korean state-sponsored hacking group, based mostly on sturdy onchain and offchain intelligence. The identical group was behind the USD 1.5 billion Bybit hack in February 2025.
- What’s EIP-7702, and the way was it used?
EIP-7702 lets an atypical Ethereum pockets run a wise contract’s code by signing an authorization. The attacker used a pre-signed authorization to make a Binance sizzling pockets run a sweeper contract that solely the attacker may name, then used it to empty the pockets and to maintain sweeping new funds that arrived later.
- How a lot of the stolen crypto has been frozen?
Tether, Circle, Ripple and World Liberty Monetary have frozen about USD 2.67 billion in stablecoins, and Arbitrum’s Safety Council has frozen about USD 30 million in ETH and ARB, roughly USD 2.7 billion in whole. The attacker nonetheless controls greater than 420,000 ETH and 18,270 BTC, price about USD 2.4 billion, plus smaller quantities on different chains.
- How does this evaluate to different main hacks?
At about USD 6.36 billion, that is the largest crypto theft on report, about 4 instances the USD 1.5 billion Bybit hack of February 2025. Even after the stablecoin freezes, the quantity the attacker nonetheless holds exceeds any earlier theft.